Cybersecurity in Finance: Defending Against AI-Powered Phishing
The financial sector has always been a primary target for cybercriminals. Where the money goes, the thieves follow. However, the landscape of digital theft has evolved dramatically. Gone are the days of poorly translated emails from "foreign royalty" asking for a quick wire transfer. Today, financial institutions are battling a much more sophisticated and insidious threat: AI-powered phishing.
As generative Artificial Intelligence (AI) becomes more accessible, cybercriminals are leveraging it to craft highly convincing, hyper-personalized attacks at scale. For the finance industry, defending against AI-powered phishing is no longer optional - it is a critical imperative.
The Evolution of Phishing: From Bulk to AI Precision
Traditional phishing relied on the "spray and pray" method. Attackers would send millions of generic emails hoping a fraction of a percent would click a malicious link. These emails were often riddled with typos and generic greetings.
AI has changed the game completely. Cybercriminals now use Large Language Models (LLMs) to write flawless, contextually accurate emails. By scraping public data from LinkedIn, corporate websites, and social media, AI can generate spear-phishing emails that reference recent business deals, organizational restructurings, or specific colleagues. The result is an attack that looks and sounds exactly like a legitimate internal communication.
Why Financial Institutions Are Prime Targets
Financial institutions - banks, investment firms, wealth management companies - handle the two most valuable assets in the digital economy: money and sensitive Personal Identifiable Information (PII).
A successful phishing attack in the finance sector can lead to:
- Direct Financial Loss: Unauthorized wire transfers and drained accounts.
- Data Breaches: Exposure of customer financial records, leading to severe regulatory fines (like GDPR or CCPA).
- Reputational Damage: Loss of consumer trust, which is the foundational currency of any financial institution.
Because the potential payout is astronomical, threat actors are willing to invest in sophisticated AI tools to breach financial defenses.
Types of AI-Powered Phishing Attacks in Finance
The application of AI in social engineering goes beyond just writing better emails. Attackers are using AI across multiple vectors:
1. Scalable Spear Phishing and Whaling
AI tools automate the reconnaissance phase of an attack. They can analyze a target's communication style and draft "Whaling" emails (targeting C-suite executives) that mimic the tone and vocabulary of a CEO or CFO, urgently requesting a funds transfer to a "new vendor."
2. Deepfake Audio and Video (Advanced BEC)
Business Email Compromise (BEC) has been elevated by AI voice cloning and video deepfakes. Attackers have successfully used AI to clone the voice of a company director, calling a subordinate to authorize a multi-million dollar transfer. As these technologies improve, verifying identity over phone or video calls is becoming increasingly difficult.
3. Smishing and Vishing via Chatbots
AI-driven chatbots are deployed to conduct SMS phishing (Smishing) or voice phishing (Vishing) campaigns. These bots can hold interactive, real-time conversations with victims, adapting their responses to manipulate the target into revealing two-factor authentication (2FA) codes or login credentials.
Defensive Strategies: Fighting AI with AI
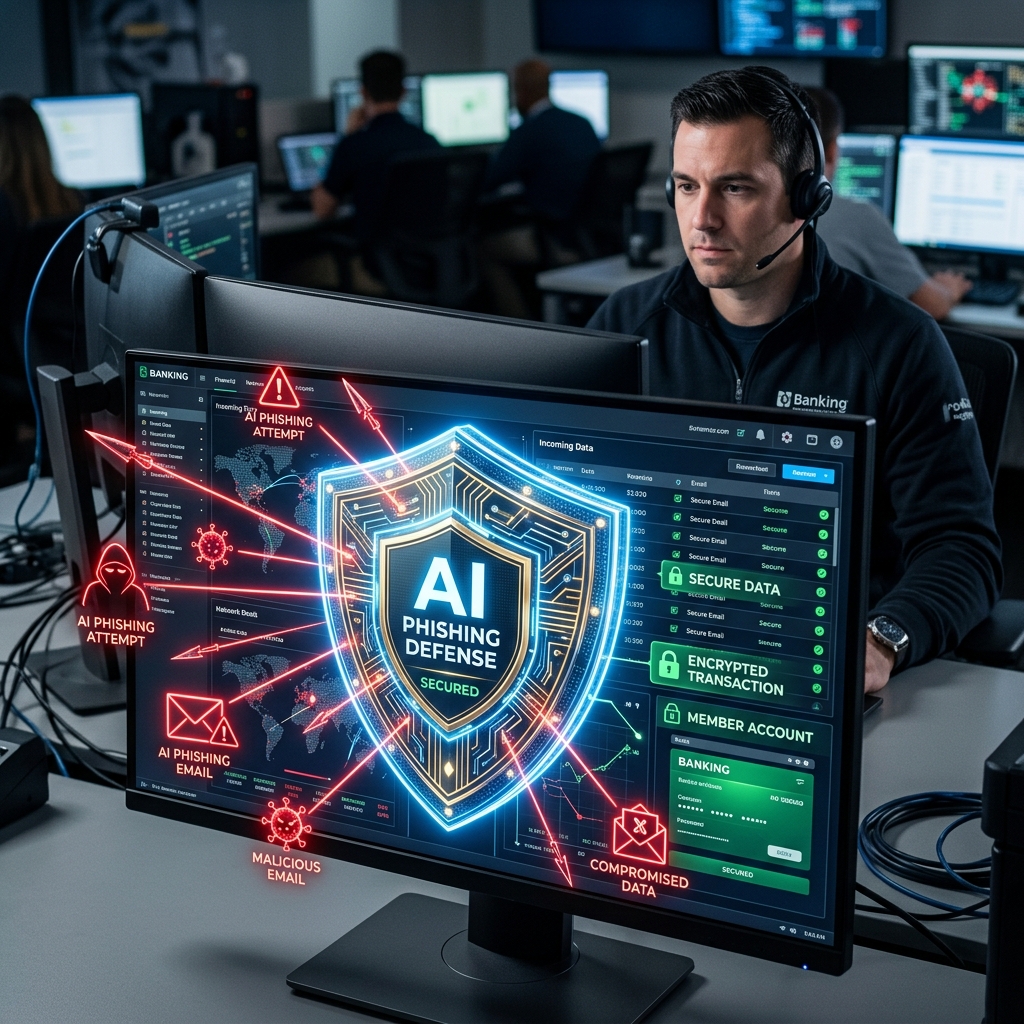
To combat AI-generated threats, financial institutions must upgrade their cybersecurity arsenals. The most effective defense strategy is to fight fire with fire - using defensive AI to detect and neutralize offensive AI.
Machine Learning for Threat Detection
Traditional Secure Email Gateways (SEGs) rely on known signatures and blacklisted domains, which are ineffective against zero-day AI attacks. Modern cybersecurity solutions utilize Machine Learning (ML) algorithms that analyze natural language processing (NLP), sender behavior, and metadata to detect anomalies that indicate a phishing attempt, even if the email comes from a seemingly legitimate domain.
Behavioral Analytics
AI-driven behavioral analytics establish a baseline of normal activity for every user in the financial institution. If an employee suddenly starts accessing sensitive databases at unusual hours or attempting unauthorized wire transfers - even if their credentials are valid - the system can flag the anomalous behavior and lock down the account.
Zero Trust Architecture
The core tenet of Zero Trust is "never trust, always verify." Financial institutions must implement continuous authentication. Even if an AI-phishing attack successfully steals a password, a robust Zero Trust framework - requiring hardware-based security keys (FIDO2) and contextual access controls - can prevent the attacker from moving laterally within the network.
The Human Element: Upgrading Security Awareness
While technology provides a crucial safety net, humans remain the last line of defense. Security Awareness Training (SAT) must be urgently updated to address AI threats.
Employees in the financial sector need to be trained to:
- Be skeptical of urgency: AI phishing often relies on manufactured urgency (e.g., "urgent wire transfer needed for an acquisition").
- Verify via out-of-band communication: If a request involves money or sensitive data, employees should verify it through a different channel (e.g., calling the sender on a known, verified phone number) before acting.
- Understand deepfakes: Staff should be aware that audio and video can be spoofed, and established protocols must be followed regardless of who appears to be making the request.
Future Outlook: The Ongoing Arms Race
The battle between cybersecurity professionals and cybercriminals is an ongoing arms race. As AI models become more sophisticated, so too will the phishing attacks directed at the financial sector. However, by investing in advanced, AI-driven defense mechanisms and fostering a culture of pervasive security awareness, financial institutions can protect their assets and maintain the trust of their clients in an increasingly complex digital landscape.